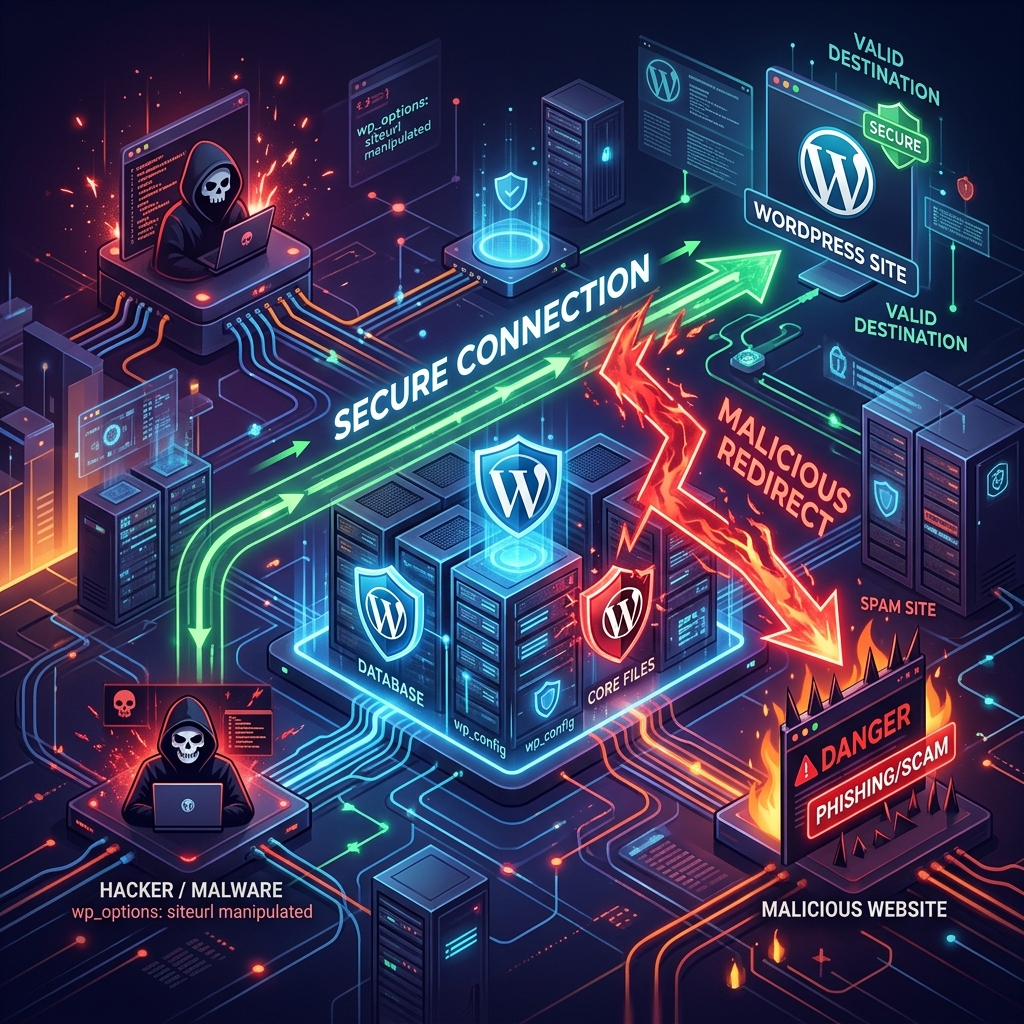
A WordPress redirect hack can be one of the most confusing signs that a website has been compromised. Your homepage may look completely normal when you visit it, yet visitors could suddenly be sent to an unfamiliar website, a spam page, a fake search engine, an online store, or a potentially dangerous site.
In some cases, the redirect happens only on mobile devices. In other cases, it occurs only when someone arrives through Google, Bing, Facebook, or another search engine. Some hacked websites redirect visitors only once, making the problem even harder to reproduce.
Need immediate help?
If your site is currently hacked or showing warnings, our incident response team can help right now.
These behaviors are often caused by malicious code hidden somewhere inside the WordPress installation.
The good news is that a WordPress redirect hack can usually be investigated and removed systematically. The key is not to simply delete the first suspicious file you find. A compromised website may contain multiple backdoors, modified WordPress files, malicious database entries, injected JavaScript, altered .htaccess rules, compromised administrator accounts, or infected plugins and themes.
Upgrade to Nexura Pro
Get enterprise-grade protection. Block zero-day exploits, advanced malware, and brute-force attacks instantly.
This guide explains how WordPress redirect hacks work, how to identify their source, how to remove them safely, and how to harden your website afterward.
What Is a WordPress Redirect Hack?
A WordPress redirect hack occurs when malicious code causes your website to send visitors somewhere other than the page they intended to visit.
For example, a visitor may enter:https://example.com/
but instead be redirected to:https://example-malicious-site.com/
The destination can change frequently. Attackers may use different domains for different visitors or rotate domains automatically.
A redirect does not necessarily mean that the entire WordPress website is visibly broken. In fact, attackers often try to keep the legitimate website functioning normally.
Their goal may be to:
- Send visitors to spam websites
- Promote questionable products or services
- Generate advertising revenue
- Distribute malware
- Steal login information
- Redirect search-engine traffic
- Manipulate search rankings
- Inject affiliate links
- Create doorway pages
- Hide malicious campaigns from administrators
- Build a persistent backdoor for future access
This is why redirect malware should be treated as a genuine security incident rather than simply a browser or caching problem.
Common Symptoms of a WordPress Redirect Hack
A hacked WordPress website does not always display an obvious warning. You may notice one or more of the following symptoms.
1. Your Homepage Redirects to Another Website
The most obvious symptom is entering your domain and being sent somewhere else. The redirect may happen immediately or after a few seconds.
For example:example.com ↓ malicious-example.com
Sometimes the destination is clearly suspicious. Other times it may look like a legitimate website.
2. Redirect Happens Only on Mobile Devices
This is a particularly common tactic. An attacker may use PHP or JavaScript to detect the visitor's user agent.
Desktop visitors may see the normal website:Desktop → WordPress website
while mobile visitors experience:Mobile → WordPress website → Malicious website
This makes the infection difficult to detect if you normally test the website from a desktop computer.
3. Redirect Happens Only From Google
Some malware attempts to identify traffic coming from search engines.
For example:Direct visitor → Normal website
Google visitor → Redirect
This technique is designed to avoid detection by the website administrator. It can also be used for SEO spam campaigns.
4. Random Pages Redirect
You may find that:example.com/about/
works normally while:example.com/blog/
redirects somewhere else.
This can happen when malicious code is inserted into a specific template, post, widget, shortcode, or database record.
5. Redirect Happens Only Once
Some redirect malware uses cookies or session information. The first visit may redirect the visitor, while subsequent visits appear normal. This makes troubleshooting particularly difficult.
6. Search Results Show Strange URLs
If your website has been compromised for a long time, search engines may discover spam pages that you never created.
Examples include URLs containing:casino viagra crypto loan gambling adult pharmacy
or thousands of random-looking URLs.
This can indicate a broader compromise beyond a simple redirect.
Why Do WordPress Redirect Hacks Happen?
WordPress itself is not automatically insecure. However, WordPress websites are frequently targeted because they are widely used and commonly include third-party themes, plugins, hosting integrations, and administrative accounts.
A redirect hack can happen through several attack paths.
Vulnerable Plugins
An outdated or vulnerable plugin may contain a security flaw that allows an attacker to upload files, execute code, modify database records, or obtain unauthorized access. Plugins should be updated regularly. Unused plugins should generally be removed instead of simply deactivated.
Vulnerable Themes
Themes can also contain security vulnerabilities. Premium themes obtained from unofficial sources are particularly risky because modified packages may contain hidden malware. Avoid downloading themes or plugins from unauthorized websites.
Weak Administrator Passwords
A compromised administrator account can give an attacker enormous control over a WordPress installation.
An attacker with administrator access may be able to:
- Install plugins
- Edit theme files
- Modify content
- Create users
- Change settings
- Inject malicious JavaScript
- Modify widgets
- Add backdoors
Use strong, unique passwords and enable multi-factor authentication whenever practical.
Compromised Hosting Accounts
Sometimes WordPress is not the original entry point. An attacker may compromise:
- cPanel
- FTP
- SFTP
- SSH
- Hosting control panels
- Database credentials
Once they gain access to the hosting environment, they may modify WordPress files directly.
Where Is Redirect Malware Usually Hidden?
One of the biggest mistakes during malware cleanup is assuming that the malicious code must be inside a single plugin. Redirect malware can exist in many locations.
.htaccess
On Apache-based hosting, .htaccess is an important file to inspect. Attackers may add redirect rules such as:
RewriteEngine On
RewriteCond %{HTTP_USER_AGENT} ...
RewriteRule ^(.*)$ https://malicious-example.com/ [R=302,L]
The exact code varies considerably. Do not delete every .htaccess file automatically. WordPress and legitimate plugins can use .htaccess. Instead, compare suspicious rules against a known-good configuration and your site's expected behavior.
wp-config.php
The wp-config.php file contains important WordPress configuration information. Attackers sometimes inject malicious PHP into it because WordPress loads this file during normal requests.
Look for unexpected code, especially code that:
- Downloads remote content
- Executes encoded strings
- Uses suspicious
eval()calls - Reads HTTP headers
- Performs conditional redirects
- Loads unknown remote resources
- Writes files
- Obfuscates large blocks of PHP
However, not every use of functions such as base64_decode() automatically means malware. Some legitimate software uses encoding functions. Context matters.
Theme Files
A redirect can be inserted into:wp-content/themes/active-theme/functions.php
or another theme file. Attackers may also modify:
header.phpfooter.phpindex.phpsingle.phppage.php- Custom template files
Malicious JavaScript is often inserted into header or footer templates.
Plugin Files
Plugins are another common location. Inspect:wp-content/plugins/
Look for:
- Recently modified files
- Unknown PHP files
- Obfuscated code
- Unexpected JavaScript
- Suspicious remote requests
- Files that do not belong to the plugin
Compare plugin files against the official package whenever possible.
WordPress Core Files
Attackers may modify core files. Commonly targeted locations can include:wp-admin/wp-includes/
and root WordPress PHP files.
A clean WordPress core installation should match the official version installed on the website. If core files have been modified, replacing them with clean copies is generally safer than attempting to manually repair every suspicious line. Be careful to preserve legitimate configuration files and user content.
Database-Injected Redirect Malware
Not all malware lives in the filesystem. Attackers can insert malicious code into the WordPress database. Potential locations include:
wp_options- Posts
- Pages
- Widgets
- Theme settings
- Custom fields
- Plugin configuration tables
The wp_options table deserves particular attention because malicious scripts can sometimes be stored there and loaded automatically. The exact table prefix may not be wp_, so do not assume that every installation uses the default prefix.
JavaScript Redirect Malware
Some redirects are implemented using JavaScript. For example, an attacker may inject JavaScript into:
- Theme templates
- Widgets
- Custom HTML blocks
- Database content
- Plugin settings
- Header/footer injection systems
A simplified example might look like:window.location.href = "https://example.com";
Real-world malware is often more sophisticated and may obfuscate the destination. Never assume that every window.location reference is malicious. Legitimate applications may use JavaScript navigation.
PHP-Based Redirect Malware
PHP malware may execute before WordPress renders the requested page. Attackers can use conditions such as:
- Is the visitor on mobile?
- Did they come from Google?
- Is the visitor logged in?
- Has the visitor seen the redirect before?
- What country is the visitor from?
Then the malware decides whether to redirect. This explains why the website may work correctly for the administrator while ordinary visitors experience malicious behavior.
How to Confirm a WordPress Redirect Hack
Before modifying files, gather evidence.
Step 1: Test Multiple Devices
Test the website using:
- Desktop
- Mobile
- Different browsers
- Private/incognito mode
If possible, test using a different internet connection.
Step 2: Test Direct and Search Traffic
Open the URL directly. Then test the same page from a search engine result. If only search traffic redirects, the infection may be using referrer detection.
Step 3: Check Browser Developer Tools
Open Chrome DevTools:F12 → Network
Reload the page and inspect requests. Look for:
- HTTP 301
- HTTP 302
- Unexpected JavaScript
- Unknown external domains
- Suspicious scripts
- Requests occurring immediately before the redirect
A redirect may be visible in the Network request chain.
Step 4: Check HTTP Headers
You can also inspect the response headers. Look for:Location:
A server-side redirect may look like:HTTP/1.1 302 Found
Location: https://malicious-example.com/
If the server itself is returning the redirect, investigating PHP, .htaccess, server configuration, and hosting-level rules becomes especially important.
WordPress Redirect Hack Removal: Safe Cleanup Process
The safest approach is systematic. Do not start randomly deleting files.
1. Take a Backup
Before making changes, create a complete backup. Ideally preserve:
- WordPress files
- Database
- Uploads
- Configuration
- Logs
A backup gives you a recovery point if a legitimate file is accidentally removed. If the site is actively compromised, keep a copy of the infected state separately for investigation.
2. Put the Website Into Maintenance Mode
If practical, temporarily restrict public access during cleanup. This reduces the risk to visitors while you investigate. For high-risk infections, consider placing the site behind an appropriate access restriction or maintenance page.
3. Scan the Website
Use a reputable malware scanner to identify suspicious files. A good scanner should ideally examine more than filenames. Useful detection techniques can include:
- File integrity checking
- Malware signatures
- Suspicious code patterns
- Known malicious hashes
- PHP analysis
- Database scanning
- Configuration inspection
Do not blindly delete every file flagged by a scanner. False positives are possible.
4. Compare WordPress Core Files
If the WordPress core has been modified, replace the core files with clean copies of the same WordPress version. Avoid overwriting:wp-content/wp-config.php
without understanding what you are doing. The goal is to restore trusted core files while preserving legitimate site data.
5. Reinstall Suspicious Plugins
If a plugin appears compromised, the safest approach is often:
- Record its configuration.
- Obtain the plugin from its legitimate source.
- Remove the existing plugin files.
- Install a clean version.
- Update it.
- Check whether the vulnerability that allowed the compromise still exists.
Simply replacing one malicious file may leave a backdoor elsewhere.
6. Review the Active Theme
Obtain the theme from its legitimate source. Compare suspicious files against the clean version. Pay particular attention to:functions.php, header.php, footer.php, index.php
Also check child themes if your website uses one.
7. Inspect .htaccess
Create a clean copy of the expected WordPress rewrite rules when appropriate. A standard WordPress installation often has rules similar to:
# BEGIN WordPress
<IfModule mod_rewrite.c>
RewriteEngine On
RewriteBase /
RewriteRule ^index\.php$ - [L]
RewriteCond %{REQUEST_FILENAME} !-f
RewriteCond %{REQUEST_FILENAME} !-d
RewriteRule . /index.php [L]
</IfModule>
# END WordPress
Your site's configuration may legitimately contain additional rules. Therefore, do not blindly replace .htaccess if you rely on custom redirects, caching, security controls, or hosting-specific settings.
8. Search for Suspicious Code
If you have SSH or command-line access, searching the WordPress directory can help. For example:grep -Rni --exclude-dir=node_modules "eval(" public_html/
You can also investigate suspicious encoding functions:grep -Rni --exclude-dir=node_modules "base64_decode" public_html/
Other functions worth investigating include:assert(), preg_replace(), create_function(), shell_exec(), system(), passthru(), proc_open(), popen()
But these searches are indicators, not proof of infection. Legitimate software can use some of these functions.
9. Look for Recently Modified Files
File timestamps can help identify suspicious changes. For example:find public_html -type f -mtime -14
This lists files modified within the last 14 days. If you know approximately when the attack occurred, adjust the time period. Remember that timestamps can be manipulated, and normal updates also modify many files. Use timestamps as evidence, not as the sole detection method.
10. Inspect the Uploads Directory
A particularly important location is:wp-content/uploads/
Normally, this directory primarily contains media and other uploaded content. Unexpected PHP files deserve investigation. For example:wp-content/uploads/2026/09/image.php
would be suspicious in many WordPress installations. However, hosting environments and plugins can differ, so investigate before deleting files.
11. Check Administrator Accounts
Open:Users → All Users
Look for accounts you do not recognize. Also check:
- Administrator roles
- User creation dates
- Password changes
- Application passwords
- API access
- Suspicious sessions
Remove unauthorized accounts after preserving evidence if needed.
12. Change Credentials
After cleaning the website, change relevant credentials. This can include:
- WordPress administrator passwords
- Hosting passwords
- FTP/SFTP passwords
- SSH credentials
- Database passwords
- API keys
- Application passwords
If the attacker still has valid credentials, malware can return even after successful file cleanup.
Database Cleanup
Database cleanup should be handled carefully. Always create a database backup first. Search for suspicious:
<script><iframe>- Unexpected JavaScript
- Unknown domains
- Redirect URLs
- Encoded payloads
- Suspicious administrator records
- Modified options
Do not simply run a global SQL replacement against every occurrence of suspicious text. Serialized WordPress data can become corrupted if modified incorrectly. When editing serialized data, use tools that understand serialization.
Check wp_options
The options table deserves special attention. Look for unusual option names and unexpectedly large values. Also inspect:autoload
values where appropriate. A malicious option may contain a payload that is loaded on many requests. However, some legitimate plugins have large or complex options, so context is essential.
Clear Caches
After removing malware, clear all relevant caches. Potential cache layers include:
- WordPress cache plugins
- Server-side caching
- CDN caching
- Object cache
- Browser cache
- Hosting cache
A cached malicious response can make a cleaned website appear infected. Do not assume that clearing the cache fixes the malware. Cache clearing should happen after the underlying problem is addressed.
Check Your CDN and DNS
If you use a CDN or proxy service, inspect its configuration. Check for:
- Redirect rules
- Page rules
- Workers/functions
- Transform rules
- DNS changes
- Unexpected forwarding rules
A redirect does not always originate inside WordPress. If WordPress looks clean but the redirect continues, investigate the hosting and CDN layers.
Check Hosting Configuration
If the website continues redirecting after WordPress cleanup, investigate the server. Depending on your hosting environment, relevant configuration can include:
- Apache
- Nginx
- PHP
- VirtualHost configuration
- Control panel redirects
- Cron jobs
- Server-level rewrite rules
Also inspect scheduled tasks. An attacker may install a cron job that restores deleted malware periodically.
WordPress Cron and Server Cron
WordPress scheduled tasks can be legitimate. Look for unexpected scheduled actions created by unknown plugins or malicious code. At the server level, inspect cron jobs if you have permission. A malicious cron job might periodically download or recreate an infected file. This is one reason why deleting a single malicious file may not permanently solve the problem.
Check for Backdoors
A backdoor allows an attacker to regain access after the initial malware is removed. Backdoors can be:
- PHP files
- Hidden administrator accounts
- Modified plugins
- Modified themes
- Cron jobs
- Obfuscated code
- Web shells
- Database payloads
Search for unexpected files and code across the entire WordPress installation. A successful cleanup should focus on the attacker's persistence mechanism, not just the visible redirect.
Why Malware Sometimes Comes Back
One of the most frustrating situations is:
“I removed the malware, but the redirect came back.”
This usually means something was missed. Common causes include:
- Another infected file: The first malicious file was removed, but another backdoor remained.
- Compromised credentials: The attacker still has access.
- Vulnerable plugin: The original vulnerability remains exploitable.
- Server-level persistence: A cron job or hosting-level script restores the malware.
- Database infection: A malicious payload remains in the database.
- CDN redirect: The redirect is being generated outside WordPress.
- Cached response: A stale malicious response is still being served.
A recurring infection should always trigger a deeper investigation.
How to Prevent Future WordPress Redirect Hacks
Cleaning an infected site is only half the job. The next step is improving security.
Keep WordPress Updated
Update:
- WordPress core
- Plugins
- Themes
- PHP
- Server software
Security updates should not be ignored.
Remove Unused Plugins and Themes
Every additional component increases the site's attack surface. If you are no longer using a plugin or theme, remove it rather than leaving it installed indefinitely. Do not keep dozens of inactive plugins “just in case.”
Use Trusted Sources
Download plugins and themes from reputable sources. Avoid pirated or “nulled” plugins and themes. A free package may appear attractive, but modified software can contain backdoors that are extremely difficult to detect.
Use Strong Authentication
Use strong unique passwords. Where possible, enable:
- Multi-factor authentication
- Login protection
- Rate limiting
- CAPTCHA or bot protection where appropriate
Protect administrator accounts especially carefully.
Restrict File Editing
WordPress administrators can sometimes edit plugin and theme files through the dashboard. For environments where this functionality is unnecessary, consider disabling file editing:define('DISALLOW_FILE_EDIT', true);
This does not replace proper security controls, but it can reduce one avenue for code modification.
Use Least Privilege
Not every WordPress user needs administrator access. Assign the lowest role necessary.
- Administrator: Full site management
- Editor: Content management
- Author: Own content
- Contributor: Limited content creation
- Subscriber: Basic account
Reducing unnecessary privileges can limit the impact of compromised accounts.
Monitor File Integrity
File integrity monitoring can alert you when important WordPress files change unexpectedly. This is especially useful for:
- Core files
- Plugins
- Themes
- Configuration files
A security system can compare files against known-good versions or monitor suspicious changes.
Use a WordPress Security Scanner
A security scanner can help identify:
- Malware
- Modified files
- Vulnerabilities
- Suspicious code
- Security configuration problems
- Unauthorized changes
For WordPress websites that receive regular traffic, automated scanning can provide an additional layer of protection.
How Nexura Security Can Help
Nexura Security is designed as a WordPress security solution that can help website administrators monitor and protect their WordPress installations.
Security tools can be useful for detecting suspicious files, identifying potential malware, applying security hardening measures, and monitoring common attack indicators. However, no security plugin should be treated as a substitute for secure hosting, updates, backups, strong authentication, and good administrator practices.
The best approach is layered security. A WordPress security strategy can include:
Secure Hosting ↓ Updated WordPress ↓ Trusted Plugins/Themes ↓ Strong Authentication ↓ Firewall / Login Protection ↓ Malware Scanning ↓ File Integrity Monitoring ↓ Regular Backups ↓ Continuous Monitoring
This layered approach makes it harder for attackers to compromise the website and easier to identify problems when they occur.
Google Search Console After a Redirect Hack
A redirect hack can create serious SEO problems. If search engines detect suspicious redirects or spam pages, your website's search visibility can be affected.
After cleaning the site:
- Verify that the malicious redirects are gone.
- Check important URLs manually.
- Inspect indexed pages.
- Review security or manual-action notifications.
- Request re-crawling of corrected pages where appropriate.
- Continue monitoring for newly generated spam URLs.
Do not attempt to hide the infection from search engines. The correct approach is to remove the malicious content and restore the site's legitimate behavior.
What About the WordPress Site Showing a Security Warning?
Sometimes visitors may see a browser or search-engine warning after a website has been compromised. This can happen when a site is identified as distributing malicious content, phishing content, or unwanted software.
Cleaning the website is the first priority. After confirming that the site is clean, administrators can follow the appropriate review or reconsideration process provided by the relevant platform.
WordPress Redirect Hack Removal Checklist
Use the following checklist during an incident.
Detection
- Test desktop and mobile
- Test different browsers
- Test incognito mode
- Test direct traffic
- Test search-engine traffic
- Inspect browser Network requests
- Check HTTP status codes
- Look for unexpected Location headers
File Investigation
- Back up the website
- Inspect
.htaccess - Inspect
wp-config.php - Scan WordPress core
- Check plugins
- Check themes
- Check uploads
- Search for suspicious PHP files
- Review recently modified files
Database Investigation
- Back up the database
- Inspect
wp_options - Review suspicious URLs
- Check widgets
- Check posts/pages
- Check custom fields
- Look for injected scripts
Account Security
- Check administrator accounts
- Remove unauthorized accounts
- Reset passwords
- Revoke suspicious sessions
- Review application passwords
- Change hosting credentials
- Change FTP/SFTP credentials
- Rotate API keys where necessary
Server Security
- Check cron jobs
- Check server redirects
- Check CDN rules
- Check DNS
- Check hosting configuration
- Check PHP configuration
Recovery
- Replace infected core files
- Reinstall compromised plugins
- Reinstall compromised themes
- Remove backdoors
- Clear caches
- Rescan the website
- Test redirects again
- Monitor the site after cleanup
Should You Delete the Entire WordPress Website?
Not necessarily. Deleting everything may seem like the easiest solution, but it can create additional problems. You may lose: Content, Media, Configuration, WooCommerce data, Custom functionality, Theme modifications, Plugin settings, and Customer information.
A controlled rebuild from known-good components can sometimes be the safest solution for a severely compromised website. For smaller websites, a clean rebuild may be practical. For complex WooCommerce or membership websites, forensic investigation and controlled remediation may be preferable. The right decision depends on the extent of the compromise and the availability of trustworthy backups.
Can a Backup Be Used to Fix a Redirect Hack?
Yes, if the backup is known to be clean. A backup created after the infection occurred may simply restore the malware.
Before restoring a backup, determine:
- When the infection started
- When the backup was created
- Whether the backup contains modified files
- Whether the database was infected
- Whether administrator credentials were compromised
After restoration, update all software and change credentials.
How Long Does WordPress Redirect Malware Removal Take?
The time required depends heavily on the infection. A simple .htaccess modification may be resolved relatively quickly. A serious compromise involving multiple backdoors, database injections, modified plugins, modified core files, unknown administrator accounts, and server-level persistence can require significantly more investigation.
The goal should not be to remove suspicious code as quickly as possible. The goal should be to restore the website to a trustworthy state.
When Should You Hire a WordPress Security Professional?
Consider professional assistance when:
- The redirect keeps returning
- Multiple files are infected
- You cannot identify the original entry point
- The database contains malicious code
- Administrator accounts were compromised
- The hosting account may be compromised
- Customer data may have been exposed
- The site is an important business website
- The infection affects WooCommerce
- Search-engine warnings remain after cleanup
Professional remediation should include more than deleting a few suspicious files. A proper investigation should attempt to determine how the attacker gained access and whether they retained access.
Frequently Asked Questions
What is the fastest way to remove a WordPress redirect hack?
First identify where the redirect originates. Check HTTP responses, .htaccess, WordPress files, plugins, themes, database content, CDN rules, and server configuration. Do not simply delete the visible redirect URL from one file.
Why does my WordPress website redirect only on mobile?
Attackers frequently use conditional logic based on the visitor's device, browser, referrer, IP address, or cookies. This technique helps malware avoid detection. Testing only from a desktop computer may therefore produce a false sense that the website is clean.
Can a WordPress plugin cause redirects?
Yes. A vulnerable or compromised plugin can modify PHP files, inject JavaScript, alter the database, or create redirect rules. However, legitimate plugins can also create redirects, so the presence of a redirect does not automatically prove that a particular plugin is malicious.
Can .htaccess cause a WordPress redirect?
Yes. Apache rewrite rules can redirect visitors using HTTP status codes such as 301 and 302. If you find an unexpected redirect rule in .htaccess, investigate when and how it was added.
Can malware be hidden in the WordPress database?
Yes. Attackers can store malicious content in options, posts, widgets, custom fields, and plugin settings. A filesystem-only scan may therefore miss some infections.
Why does my site look clean to me but redirect visitors?
The malware may be using conditional logic. It might redirect only: Mobile visitors, Search-engine visitors, Logged-out users, Visitors from certain countries, or First-time visitors. Attackers use these techniques to make detection more difficult.
Will reinstalling WordPress remove the hack?
It may remove modified WordPress core files, but reinstalling WordPress alone does not guarantee that the site is clean. Malware may remain in: wp-content/, database, uploads/, themes/, plugins/, .htaccess, server configuration. Compromised credentials can also allow the attacker to reinfect the site.
Should I delete suspicious PHP files?
Not automatically. First determine what the file is, where it came from, and whether it belongs to legitimate software. If a file is confirmed malicious, remove it or replace the affected software with a trusted clean copy.
Does changing the WordPress password fix redirect malware?
Changing the password is important, but it does not remove existing malware. If a backdoor remains, an attacker may regain access even after the password has been changed. Credential rotation should be part of a broader cleanup process.
Can Cloudflare cause a redirect?
Yes, depending on the configuration. Redirect rules, workers, functions, page rules, or other edge configuration can potentially generate redirects. If WordPress is clean but the redirect continues, investigate the CDN and DNS layer.
How can I stop a WordPress redirect hack from coming back?
The most important steps are: Find and remove all malicious code. Identify the original attack vector. Patch vulnerable software. Remove unused plugins and themes. Secure administrator accounts. Rotate compromised credentials. Monitor file changes. Scan the website regularly. Maintain clean backups. Monitor the server and CDN configuration.
Final Thoughts
A WordPress redirect hack is more than an annoying redirect. It can be evidence that an attacker has obtained unauthorized access to your website and may have installed persistent malware. The visible redirect is often only the symptom.
The real problem may be a vulnerable plugin, compromised administrator account, modified .htaccess file, infected theme, malicious database record, hidden backdoor, compromised hosting account, or a combination of several issues.
For that reason, effective WordPress redirect hack removal should follow a structured process:
Detect → Investigate → Contain → Clean → Secure → Verify → Monitor
Do not stop after the redirect disappears. A website should be rescanned and tested from multiple devices and traffic sources. Important files should be compared against trusted versions. Credentials should be rotated when compromise is suspected. Vulnerabilities should be patched, and unnecessary attack surfaces should be removed.
Most importantly, continue monitoring after the cleanup. A clean website today can become compromised again tomorrow if the original vulnerability remains unresolved. With regular updates, secure authentication, trusted software, reliable backups, malware scanning, firewall protection, and file integrity monitoring, WordPress administrators can significantly reduce the risk of recurring infections.
If your WordPress website is unexpectedly redirecting visitors, treat the issue seriously and begin the investigation as soon as possible. The earlier a compromise is identified, the easier it is to contain, clean, and recover the website.