In the high-stakes world of cybersecurity, few terms strike as much fear into the hearts of IT professionals and website owners as the "Zero-Day Vulnerability". If you run a WordPress website—whether it's a high-traffic corporate blog, an enterprise WooCommerce store, or a digital publication—understanding and mitigating zero-day threats is not just an option; it's a critical business survival requirement.
With WordPress powering over 43% of all websites on the internet, it is undoubtedly the most targeted Content Management System (CMS) globally. While WordPress core is generally highly secure, the ecosystem of over 60,000 plugins and thousands of themes creates a massive, often poorly coded attack surface. Today, we are diving deep into the anatomy of zero-day vulnerabilities in WordPress, the devastating impact they can have, and how Nexura Security Pro provides enterprise-grade protection before a patch is even released.
Need immediate help?
If your site is currently hacked or showing warnings, our incident response team can help right now.
What Exactly is a Zero-Day Vulnerability?
To understand a zero-day (0-day) vulnerability, you need to understand the timeline of software security. When a developer writes code for a WordPress plugin, they might accidentally leave a flaw—perhaps they forgot to sanitize an input field, or they failed to check user permissions before allowing a file upload.
A vulnerability becomes a zero-day when hackers discover and exploit this flaw before the developer knows about it or has had a chance to release a patch. The term "zero-day" refers to the fact that the developer has had exactly zero days to fix the issue. There is no official patch available, no warning from the plugin author, and no immediate defense mechanism built into the software.
Upgrade to Nexura Pro
Get enterprise-grade protection. Block zero-day exploits, advanced malware, and brute-force attacks instantly.
When a zero-day exploit is released into the wild, hackers automate the attack. They use massive botnets to scan millions of WordPress sites, looking for the specific vulnerable plugin. If your site has the plugin installed, you are compromised in seconds.
The Anatomy of a Zero-Day Attack
- Phase 1: Discovery. A cybercriminal (or a security researcher who sells the exploit on the dark web) finds a critical flaw in a popular WordPress plugin (e.g., an SEO plugin, a page builder, or a form plugin).
- Phase 2: Weaponization. The hacker writes an automated script (an exploit payload) designed to take advantage of the flaw. For example, the payload might bypass authentication and create a hidden administrator account.
- Phase 3: Mass Exploitation. The hacker deploys botnets to crawl the internet. The bots check the
/wp-content/plugins/directory of millions of sites. When they find the vulnerable plugin, they deploy the payload. - Phase 4: Compromise. Your site is now infected. The hacker might inject SEO spam, redirect your traffic to malicious sites, deploy ransomware, or install a credit card skimmer (Magecart) if you run WooCommerce.
Why Standard WordPress Security Fails
Most website owners believe that installing a free, legacy security plugin (like Wordfence or Sucuri) keeps them safe. However, traditional security plugins rely heavily on signature-based detection. This means they operate like an antivirus: they have a database of known malware signatures and known vulnerabilities. When a file matches a signature, it gets blocked.
The fatal flaw in this approach is that a zero-day exploit, by definition, has no signature yet. The security plugin doesn't know it exists. By the time the security vendor updates their firewall rules (which can take days or weeks), your site has already been hacked, your database compromised, and your SEO rankings destroyed.
The Vulnerability Window
The time between when a zero-day is actively exploited and when you actually apply the patch is known as the "Vulnerability Window". For many websites, this window remains open for weeks because site owners don't update their plugins daily. During this time, you are entirely defenseless against automated attacks.
How Nexura Security Defeats Zero-Day Exploits
To stop threats that have never been seen before, you need a fundamentally different approach to security. You cannot rely on reacting to known signatures; you must proactively block malicious behavior.
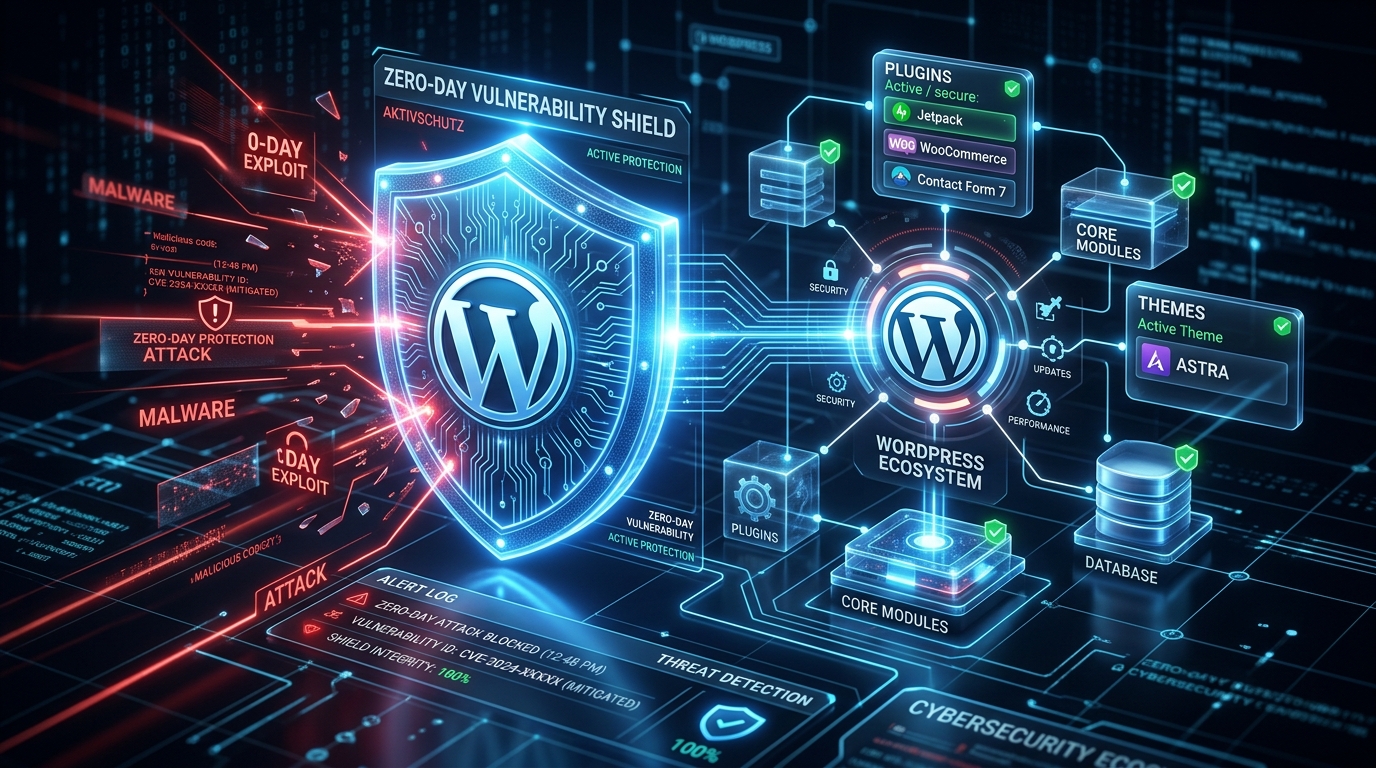
Nexura Security Pro was engineered precisely for this scenario. Instead of relying solely on reactive signatures, Nexura employs advanced heuristic analysis, behavioral blocking, and deep packet inspection via its Pre-Boot Web Application Firewall (WAF).
1. The Power of the Pre-Boot WAF
Most WordPress firewalls load as standard plugins. This means WordPress has to initialize, connect to the database, and run thousands of lines of code before the firewall even turns on. If a zero-day exists in a plugin that loads before the firewall, the firewall is useless.
Nexura's Pre-Boot WAF utilizes PHP's auto_prepend_file directive. This means Nexura intercepts and analyzes every single HTTP request at the server level, before WordPress or any plugins even begin to load. If the request contains a malicious payload (like a SQL injection or a Cross-Site Scripting attempt), Nexura drops the connection instantly, saving server resources and preventing the exploit from ever touching the vulnerable plugin.
2. Virtual Patching
When a zero-day is eventually disclosed by security researchers, the Nexura Threat Intelligence team immediately deploys Virtual Patches to all Nexura Pro users. A virtual patch is a specific WAF rule designed to block the exact exploit vector of the newly discovered vulnerability.
This means that even if you haven't updated the vulnerable plugin on your website, Nexura will intercept the attack payload and block it. You remain completely protected while you take the time to test and safely apply the official plugin update on your staging server.
3. Heuristic and Behavioral Blocking
Hackers attempting to exploit a zero-day often exhibit specific behavioral patterns. They might send malformed HTTP headers, attempt to execute unexpected PHP commands via POST requests, or try to upload files with double extensions (e.g., image.jpg.php).
Nexura doesn't need to know the specific plugin being attacked. The WAF recognizes the behavior of an exploit attempt. If an incoming request contains a Base64 encoded payload attempting to execute `eval()` or `system()` functions, Nexura blocks it universally, effectively neutralizing the zero-day attack on the spot.
Real-World Examples of Devastating Zero-Days
To illustrate the severity, let's look at how zero-day vulnerabilities have historically devastated the WordPress ecosystem:
- The File Manager Plugin Exploit (2020): A critical zero-day in a popular file manager plugin allowed unauthenticated users to upload malicious PHP files directly to the server. Over 700,000 sites were vulnerable. Within hours of the exploit going public, botnets infected hundreds of thousands of sites with ransomware and SEO spam. Sites using Pre-Boot firewalls that blocked unauthorized PHP uploads were completely unaffected.
- The Elementor Pro Vulnerability (2023): An authenticated zero-day allowed users with minimal permissions (like subscribers or customers) to upload arbitrary files or change the site's administrator email address. This led to massive site takeovers. Nexura's behavioral rules blocked the unauthorized privilege escalation attempts natively.
Best Practices to Minimize Zero-Day Risks
While Nexura Security Pro provides the ultimate safety net, adhering to security best practices is essential for reducing your overall attack surface.
- Audit Your Plugins: Every plugin is a potential entry point. Delete (don't just deactivate) any plugins you are not actively using. The fewer plugins you have, the smaller your attack surface.
- Never Use Nulled Themes or Plugins: "Free" premium plugins downloaded from third-party sites are almost always injected with backdoors. They are zero-days waiting to happen.
- Implement Least Privilege: Do not give Administrator access to users who only need to write blog posts (give them Author or Contributor roles). Limit the impact if an account is compromised.
- Disable PHP Execution in Uploads: Hackers love to upload malicious scripts into the
/wp-content/uploads/folder. Use Nexura's One-Click Hardening to disable PHP execution in this directory. - Keep Everything Updated: While it won't protect you from a true zero-day, updating immediately after a patch is released closes the "Vulnerability Window". Enable automatic updates for trusted plugins.
Conclusion: Proactive Defense is the Only Defense
In 2026, relying on signature-based scanners and reactive updates is a recipe for disaster. The speed at which cybercriminals weaponize zero-day vulnerabilities means that by the time you read about an exploit on a security blog, your site may already be compromised.
You need a security solution that operates dynamically, analyzing traffic contextually and blocking malicious intent at the edge of your server. Nexura Security Pro's Pre-Boot WAF is specifically designed to give you that unfair advantage over hackers.
Don't wait to become a statistic in the next massive WordPress vulnerability outbreak. Lock down your site today with Nexura.
Secure Your Site Against Zero-Days Today
Don't leave your enterprise or e-commerce site vulnerable to the next big exploit. Upgrade to Nexura Security Pro and get real-time, behavioral WAF protection.
Exclusive Offer
Use code NEW20 for 20% off your first year!